
Private Photo Sharing: A Safety Checklist
Private photo sharing step by step: strip the location data, check the background, then share an unlisted link that expires when you choose.
By Mudasir Ahsan (Founder) · · Updated · 9 min read
Facts checked against official sources on
On this page
Private photo sharing depends on four things you control: the location data hidden in the file, what shows in the frame, who gets the link and how long the photo stays online. Deal with those and you have done most of what can be done. Once someone else has the image you can't take their copy back. The safest photo is still the one you decide not to send.
 Photo: Towfiqu barbhuiya on Pexels
What a shared photo gives away
More than the moment it shows. Information gets out in four ways:
| What leaks | How | Example |
|---|---|---|
| Hidden metadata | GPS coordinates, date, time and device details stored inside the file | A photo of something you are selling carries your home's coordinates |
| Visible details | Things in the frame you did not notice | A house number, a school logo, a letter on the table, a screen in the background |
| The link itself | Links get forwarded, pasted in group chats or posted publicly | A link sent to one friend ends up in a forum thread |
| The service | Who stores the image, who can browse it and how long it is kept | An image posted to a public gallery is indexed and copied |
The first row is the one people can't see, and it's the easiest to fix.
The checklist
The steps run in the order you meet them: before you upload, while you share and afterwards.
- Remove location and other metadata.
- Look at the whole picture, including the background and reflections.
- Crop or cover anything sensitive with a solid block, not a light blur.
- Choose an unlisted link or a direct message over a public post or gallery.
- Set an expiry time if the photo is only needed briefly.
- Save the delete link somewhere safe.
- Send the link only to the people who need it.
- Delete the image when it has done its job.
Short on time? Do steps 1 to 3 and step 7. Those can't be fixed after the photo is out, and everything else on the list can.
How do I remove location data before sharing a photo?
Most phone photos contain EXIF metadata, and many include the exact GPS position where they were taken. The coordinates sit inside the file, so they travel with every copy of it. Apple's personal safety guide warns that people you share photos with "may be able to access the location metadata and learn where it was taken." Our explainer on what EXIF data is lists every field a typical photo carries.
How you remove it depends on where the photo is.
On an iPhone you can do it while sharing. Select the photos, tap Share, tap Options, then turn off Location. Apple's guide says "Location Not Included" then appears above the Options button. To stop the camera recording it in future photos, go to Settings > Privacy & Security > Location Services > Camera and choose Never.
Google Photos is less simple, because the answer changes with how you share. Google's help page on photo locations explains that if your camera added a location and you share the photo on Google Photos, the photo shows that location. Shared albums have a Share photo locations option, which Google says is turned off by default for new shared albums. Partner sharing is different. Google says that if you set it up, all photos you share have location details.
On any device, you can run the photo through our free EXIF remover and share the clean copy. And if you were going to share by link anyway, uploading to PictureToLink does this step for you. Every upload is re-encoded, and all embedded metadata (GPS coordinates, camera model, date taken) is discarded before the image is stored.
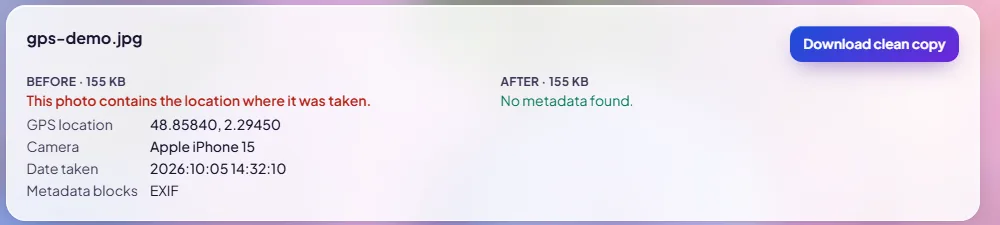
Check the Before panel: if it lists a location, remove it before you share.
Then check your work. Open the cleaned copy's info or properties panel and confirm that no map or coordinates appear.
Checking the background
Removing metadata does nothing about what is visible. Take ten seconds to look at the whole frame, then zoom in on the edges. These are the details people miss:
- House numbers, street signs and car number plates, including ones reflected in windows or seen through them.
- Documents and screens: letters, parcels with address labels, open laptops and phone notifications in the background.
- School uniforms, badges and lanyards, which can identify a school or employer.
- Views from windows. A distinctive skyline or landmark narrows down a location quickly.
- Reflections in mirrors, glasses, glossy surfaces and eyes.
- Faces of other people, especially children, who have not agreed to be shared.
If something needs to go, crop it out or cover it with a solid block. Blur feels like enough, and often it isn't. A light blur or pixelation can sometimes be partly reversed, or stay readable. For names, addresses and account numbers, use a solid box.
Shrinking the photo helps with the details you didn't spot. A 12 MP phone photo is 4032 × 3024 pixels. Resize it to 1280 px wide and you keep 1280 × 960 pixels, about 10% of the original, so a number plate that was 200 pixels across in the background is now about 63 pixels across. A plate that size is far harder to read, especially after compression. It won't hide anything large or close to the camera, though, and it's no substitute for the solid box on something you know is sensitive. If the photo is only for viewing on a phone, I'd send it at 1280 px anyway; nobody needs the full resolution to look at it.
Which private photo sharing method should I use?
Where you put the photo matters as much as what is in it. There are three broad levels of exposure:
| Sharing method | Who can find it | Good for |
|---|---|---|
| Public post or public gallery | Anyone, often including search engines | Photos you are happy for the world to see |
| Unlisted link | Only people who have the link | Sending to a few people without an account on either side |
| Private album or direct message with sign-in | Only invited accounts | Family photos, ongoing private sharing |
A Reddit post sits at the public end of that scale. Before you post an image on Reddit, go through the first three steps of the checklist, because anyone can open and save what you put there.
For a photo meant for a few people, the unlisted link is the practical middle ground. On PictureToLink, every image gets a random link that is not listed anywhere on the site. Share pages ask search engines not to index them, and they carry no ads.
"Unlisted" is often read as "private", and that's a mistake. A link is not a password. An unlisted image is hidden only because nobody can guess or look up its address. Whoever holds the address can open it and can pass it on to anyone else, with nothing to stop them. I go into that in are image links private?
Guessing isn't the real risk. Each PictureToLink address carries a random 10-character code drawn from 62 characters, about 840 quadrillion possibilities. Someone trying 1,000 codes a second gets through 60,000 in 60 seconds, which is nothing against that pool. The risk is the link being forwarded.
So the link is the wrong tool for some photos. Do not upload anything that would harm you if it became public: identity documents, bank details, intimate images or photos that reveal where children are. For those, use an end-to-end encrypted messaging app or do not share them at all.
For everything else, two habits keep a link under control. Send it in a direct message or email, and keep it out of public comments and group chats with people you do not know. Then use one link per audience. To send the same photo to two groups, upload it twice so you can delete one without affecting the other.
Expiry and delete links
Most photos only need to be online for a short time: a picture of a damaged parcel for a seller, a room photo for a landlord, a screenshot for tech support. Set an expiry and you don't have to remember to clean up.
On PictureToLink:
- Before uploading on the homepage, open the options and set Auto-delete to 1 hour, 1 day, 7 days or 30 days.
- Upload the photo and copy the link you need.
- Copy the private delete link shown under the upload and keep it somewhere safe. It is also remembered under "Recent uploads" in the browser you used, but only on that device.
Take the damaged parcel. The seller needs the picture until the claim is settled and never again, so 7 days or 30 days fits better than leaving it open. With no expiry set, the image stays online while people keep viewing it and is removed after 12 months without a single view. That is a long time for a photo of your front door.
Deleting has one limit worth knowing. A browser that already opened the image may keep its own copy for a while, and no website can reach into someone's cache. We send images set to auto-delete with a cache time of at most 300 seconds, never past their deadline, but an image without an expiry may be cached for up to 86,400 seconds, a full day, after you delete it. So set the expiry before you share, not after.
Deleting with the delete link is permanent, and every link to the image stops working. Treat that link like a key. Anyone who has it can delete the image, so never send it along with the share link.
Our guide to temporary image links suggests an expiry for common situations.
Can I undo sharing a photo?
Only partly. You can remove the photo from the places you control, but not from other people's devices.
Start with the host. Delete the image there and every link to it stops working, including the direct link, the share page and any embed codes. If it sits in a shared album, remove it from the album or stop sharing the album in the service you used. Then change your settings for next time, such as turning off camera location or location sharing in shared albums.
Misuse is a separate route. If someone has re-posted your photo somewhere else, use that site's reporting or takedown process. If it was uploaded to PictureToLink by someone else, use our report form via the FAQ.
None of that reaches a copy. If someone downloaded, saved or screenshotted the photo, deleting the original does not affect what they hold. A link that was forwarded before you deleted the image may already have been opened. And no host can promise instant removal everywhere, because copies on other sites, or in other people's apps, are outside the original host's control.
That is why the first steps on the checklist carry the most weight. The location data, the background and the list of people who get the link are the parts you fully control.